

Privacy Protection
Privacy Protection Policy and Management Mechanism
To maintain the security of personal information, TS Holdings has not only formulated regulations on the protection and management of personal information, but also reviewed the appropriateness of these regulations in accordance with the law to ensure the legal collection, processing and use of personal information of customers and employees. In addition to regularly checking the current status of personal data security maintenance and evaluating possible risks to personal data, TS Holdings also establishes appropriate management mechanisms based on the results of the risk assessment, and formulate contingency, notification, and prevention mechanisms to implement personal data protection and management measures for security incidents such as theft, alterations, damage, loss, or leakage of personal data.
Privacy Protection Measures
To enhance the ability to respond to personal data infringement incidents and raise the risk awareness of all employees, Taishin Bank, SKB, SKL and Taishin Securities has formulated the "Personal Data Infringement Incident Management Standards" to effectively implement emergency response and handling. When a personal data infringement incident occurs, the supervisor shall immediately be notified supervisor and the risk assessment and classification of the incident must be completed within the time limit. Depending on the extent of the impact of the incident, an emergency response team shall be set up for the response, coordination, liaison, and investigation of the incident. TS Holdings adopts the principle of zero tolerance for personal privacy infringement. Also, in order to respect the customers' rights to their personal data, TS Holdings' subsidiaries
have formulated "Operating Rules for Exercising the Rights of the Parties" based on their own business requirements, specify customers' personal data's inquiry, viewing, copying, supplement, correction, deletion and the right to stop collection, processing and use.
Personal Information Infringement reporting procedure (Taishin Bank example)
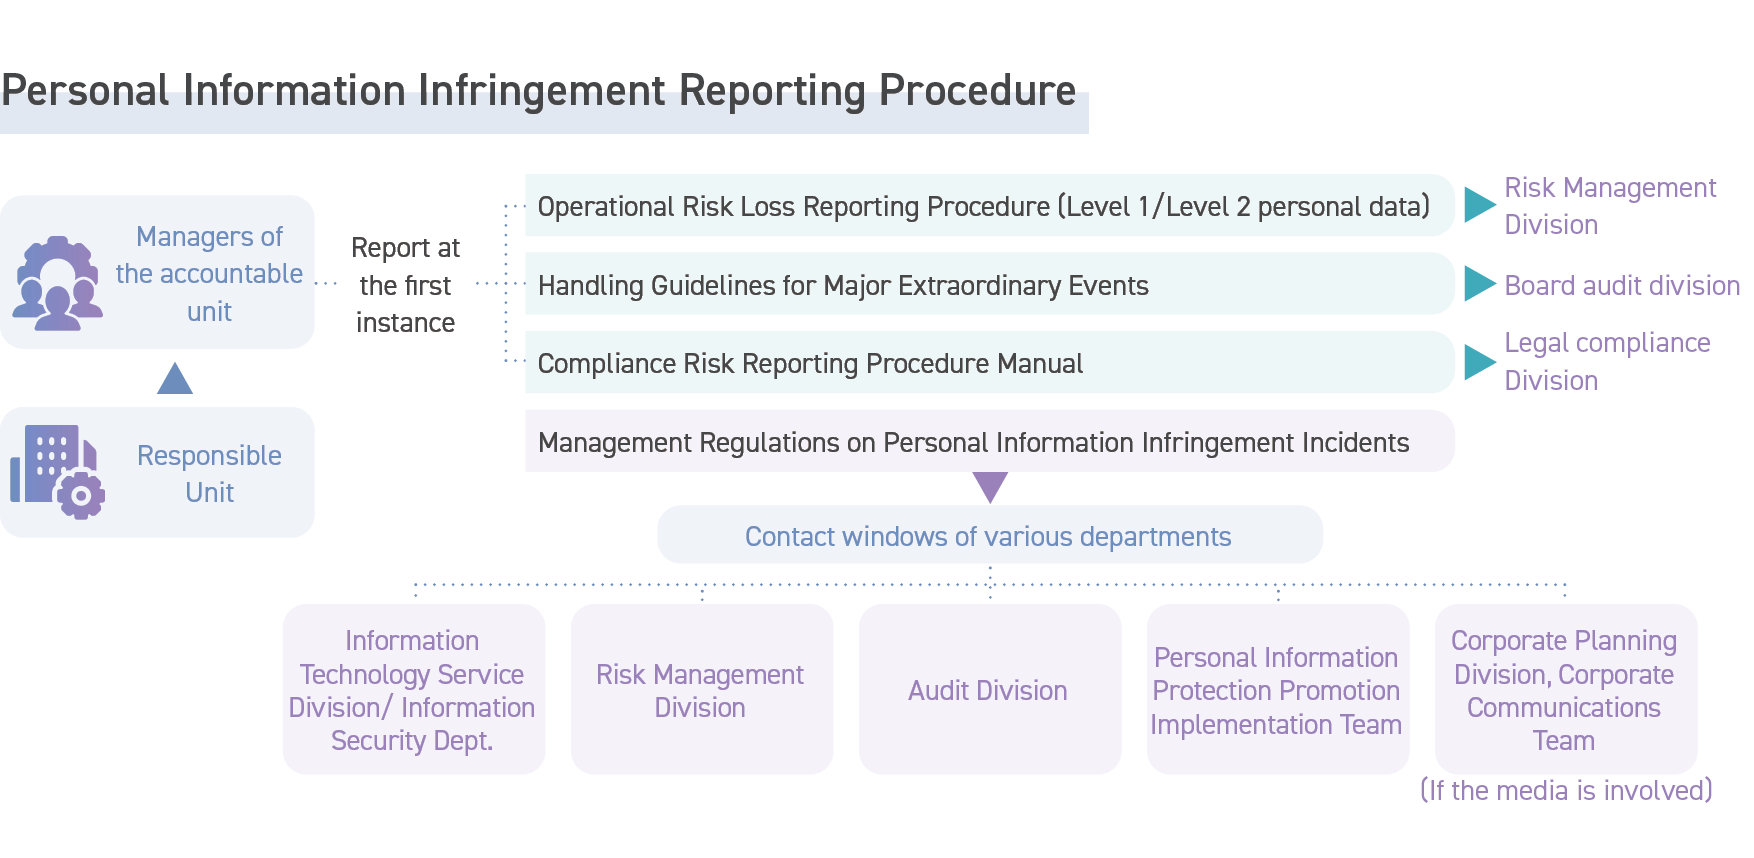
The handling of each level of incident and the reporting level
-
Level 1 (Note1)
-
Personal Information Protection Implementation Department
-
Must be handled within 2 days.
-
Supervisor of said department
-
Level 2 (Note2)
-
Emergency Response Team
-
- Notification must be completed within 12 hours.
- The emergency response team shall draw up a response plan within 2 working days.
- In accordance with the "Financial Supervisory Commission Designated Non-Government Agencies' Personal Data File Safety Maintenance Measures", report to the Financial Supervisory Commission within 72 hours for any major personal data incidents.
-
- President
- Personal Data Protection Committee members, etc.
Note 1: Level 1 incident: Less than 100 cases of security incidents such as theft, tampering, damage, loss, leakage, etc. of personal data or incidents that meet the definition of other internal regulations.
Note 2: Level 2 Incidents: Any of the following conditions: (1)Significant personal data incidents, referring to situations where the theft, alteration, damage, loss, or leakage of personal data may jeopardize the normal operations of the Bank or affect the rights and interests of a large number of individuals [100 or more cases]. (2)Incidents involving highly sensitive data (e.g., data related to public figures, etc.). (3)Incidents reported by the media.
To strengthen the awareness on personal protection and establish a corporate culture of respect for personal information, Taishin continues to promote education and training on personal information protection so that employees understand the requirements of relevant laws and regulations. Furthermore, allow employees fully understand the scope of responsibilities, mechanisms, procedures, and measures for personal information protection.
Training for Protection of Personal Information in 2025
-
New recruits (to complete training within six months after coming onboard)
-
-
"Newcomer e-learning" course: Promotion of Personal Information Protection
-
"New Employee Training" course: Introduction of Regulatory Compliance
-
-
100
-
100
-
General employees
-
-
Information Security Awareness and Personal Information Protection
-
-
100
-
100
-
Contact person for personal data (or delegate representative) for each division
-
-
Personal data inventory training
-
-
100
-
100
-
Contact person or emergency response team of personal data management for each division
-
-
Personal data violations response drills
-
-
100
-
100
Internal/External audit defects
TS Holdings and its subsidiaries all conduct personal data management operations and audits in accordance with internal control systems and personal data protection regulations. Internal and external audits as well as third-party
verification completed by each company revealed no material irregularities in 2025. Taishin Bank commissioned an accountant to conduct an audit of the implementation of personal data protection for 2025 in accordance with the agreed procedures, and no major irregularities were found after the implementation of the agreed procedures. In addition, Taishin Bank also obtained the PIMS (personal information management system) certification and ISO27701 (privacy information management standard) certification in 2024. SKB commissioned an accountant to conduct an audit of the implementation of personal data protection for 2025 in accordance with the agreed procedures, and no major irregularities were found after the implementation of the agreed procedures. Since 2019, SKL has commissioned BSI to implement BS 10012:2017 Personal Information Management System (PIMS) certification and once again passed the certification in 2025, showing that its personal information management system continues to meet international standards. Taishin Securities conducts personal information protection security project audits in accordance with the annual audit plan, and there were no major abnormalities in the audit results. Taishin Securities Investment Trust Audit Office conducted personal information protection security audits according to the annual plan, and no major abnormalities were found in the audit results.
Grievance Mechanism of Personal Information
TS Holdings attaches great importance to the protection of personal information, and customers can raise questions or file complaints through different channels. If the results of an investigation confirm a violation of personal information, we will take disciplinary actions (e.g., downgrading of performance evaluation, withholding of bonuses, and internal penalties). We shall also propose specific system and process improvements to address the root cause of the complaint and avoid the recurrence of similar situations. Quarterly reporting will be made to the Treating Customers Fairly Committee for continuous monitoring and improvement.
